Frameworks and controls
Thirteen frameworks ready to adopt, and your own on top. A control library based on ISO 27001 Annex A, with test plans and results.

Built in the EU, for EU regulation.
Atitic is a compliance workspace for EU companies and the consultancies that serve them: GDPR, NIS2, DORA, ISO 27001 and nine more frameworks, with the policies, evidence, controls and records that prove them.
No payment details to start. Data hosted in the EU. Confirm your email within 7 days to keep the workspace.
From the first framework to the audit, in the same workspace.
Answer questions about your organization. Fasttrack shows which frameworks apply and why, then sets up the programs, starter policies, controls, registers and a first task plan in one run. You review every item before it is created.
Policies, evidence, controls, risks and register records are linked to the requirements they meet. Evidence keeps its versions, its SHA-256 fingerprint and who reviewed it. Crosswalks show where the same work also counts for another framework.
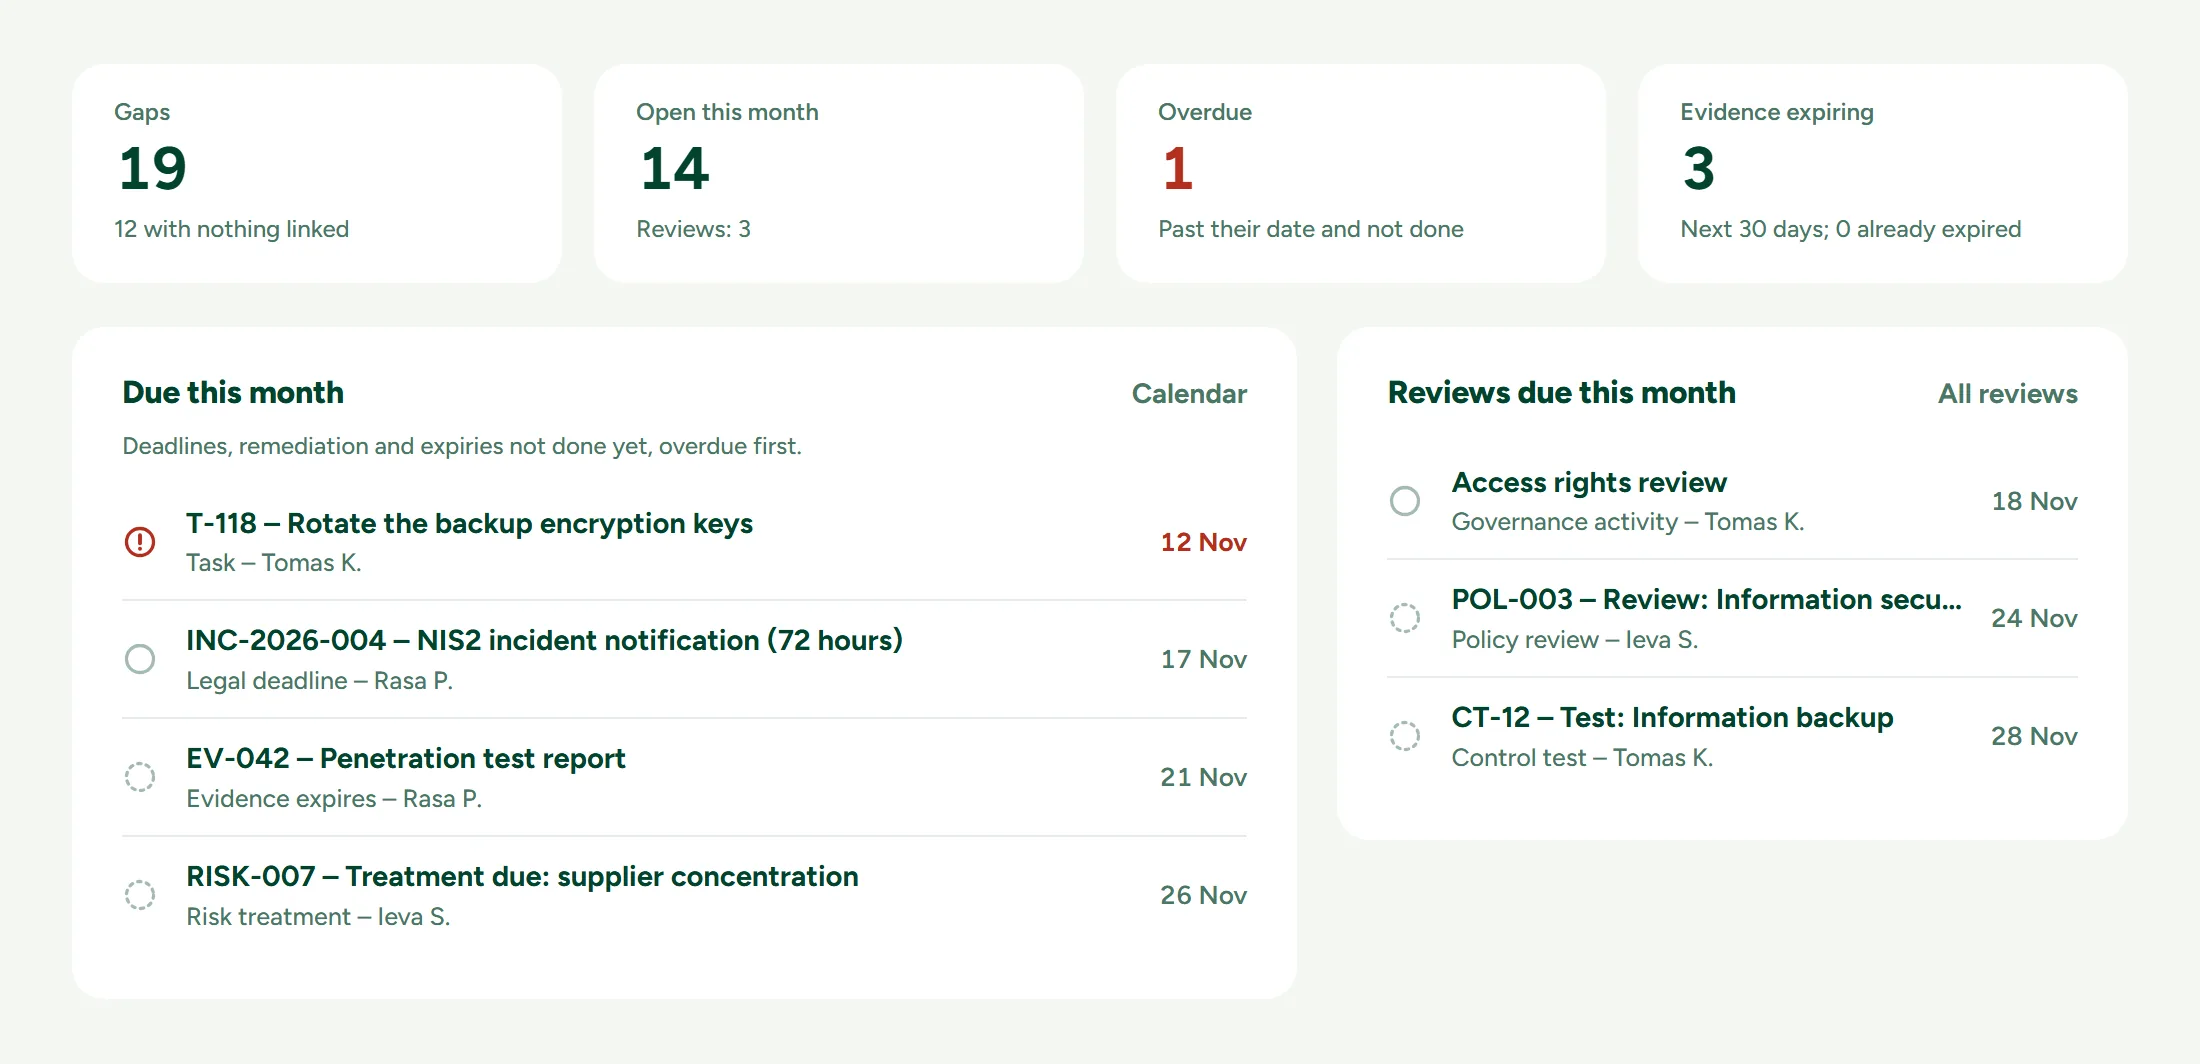
Reviews, control tests, policy renewals, task deadlines and legal reporting clocks sit in one governance calendar, with reminders to the people who own them. Subscribe to it from Outlook or Google Calendar.
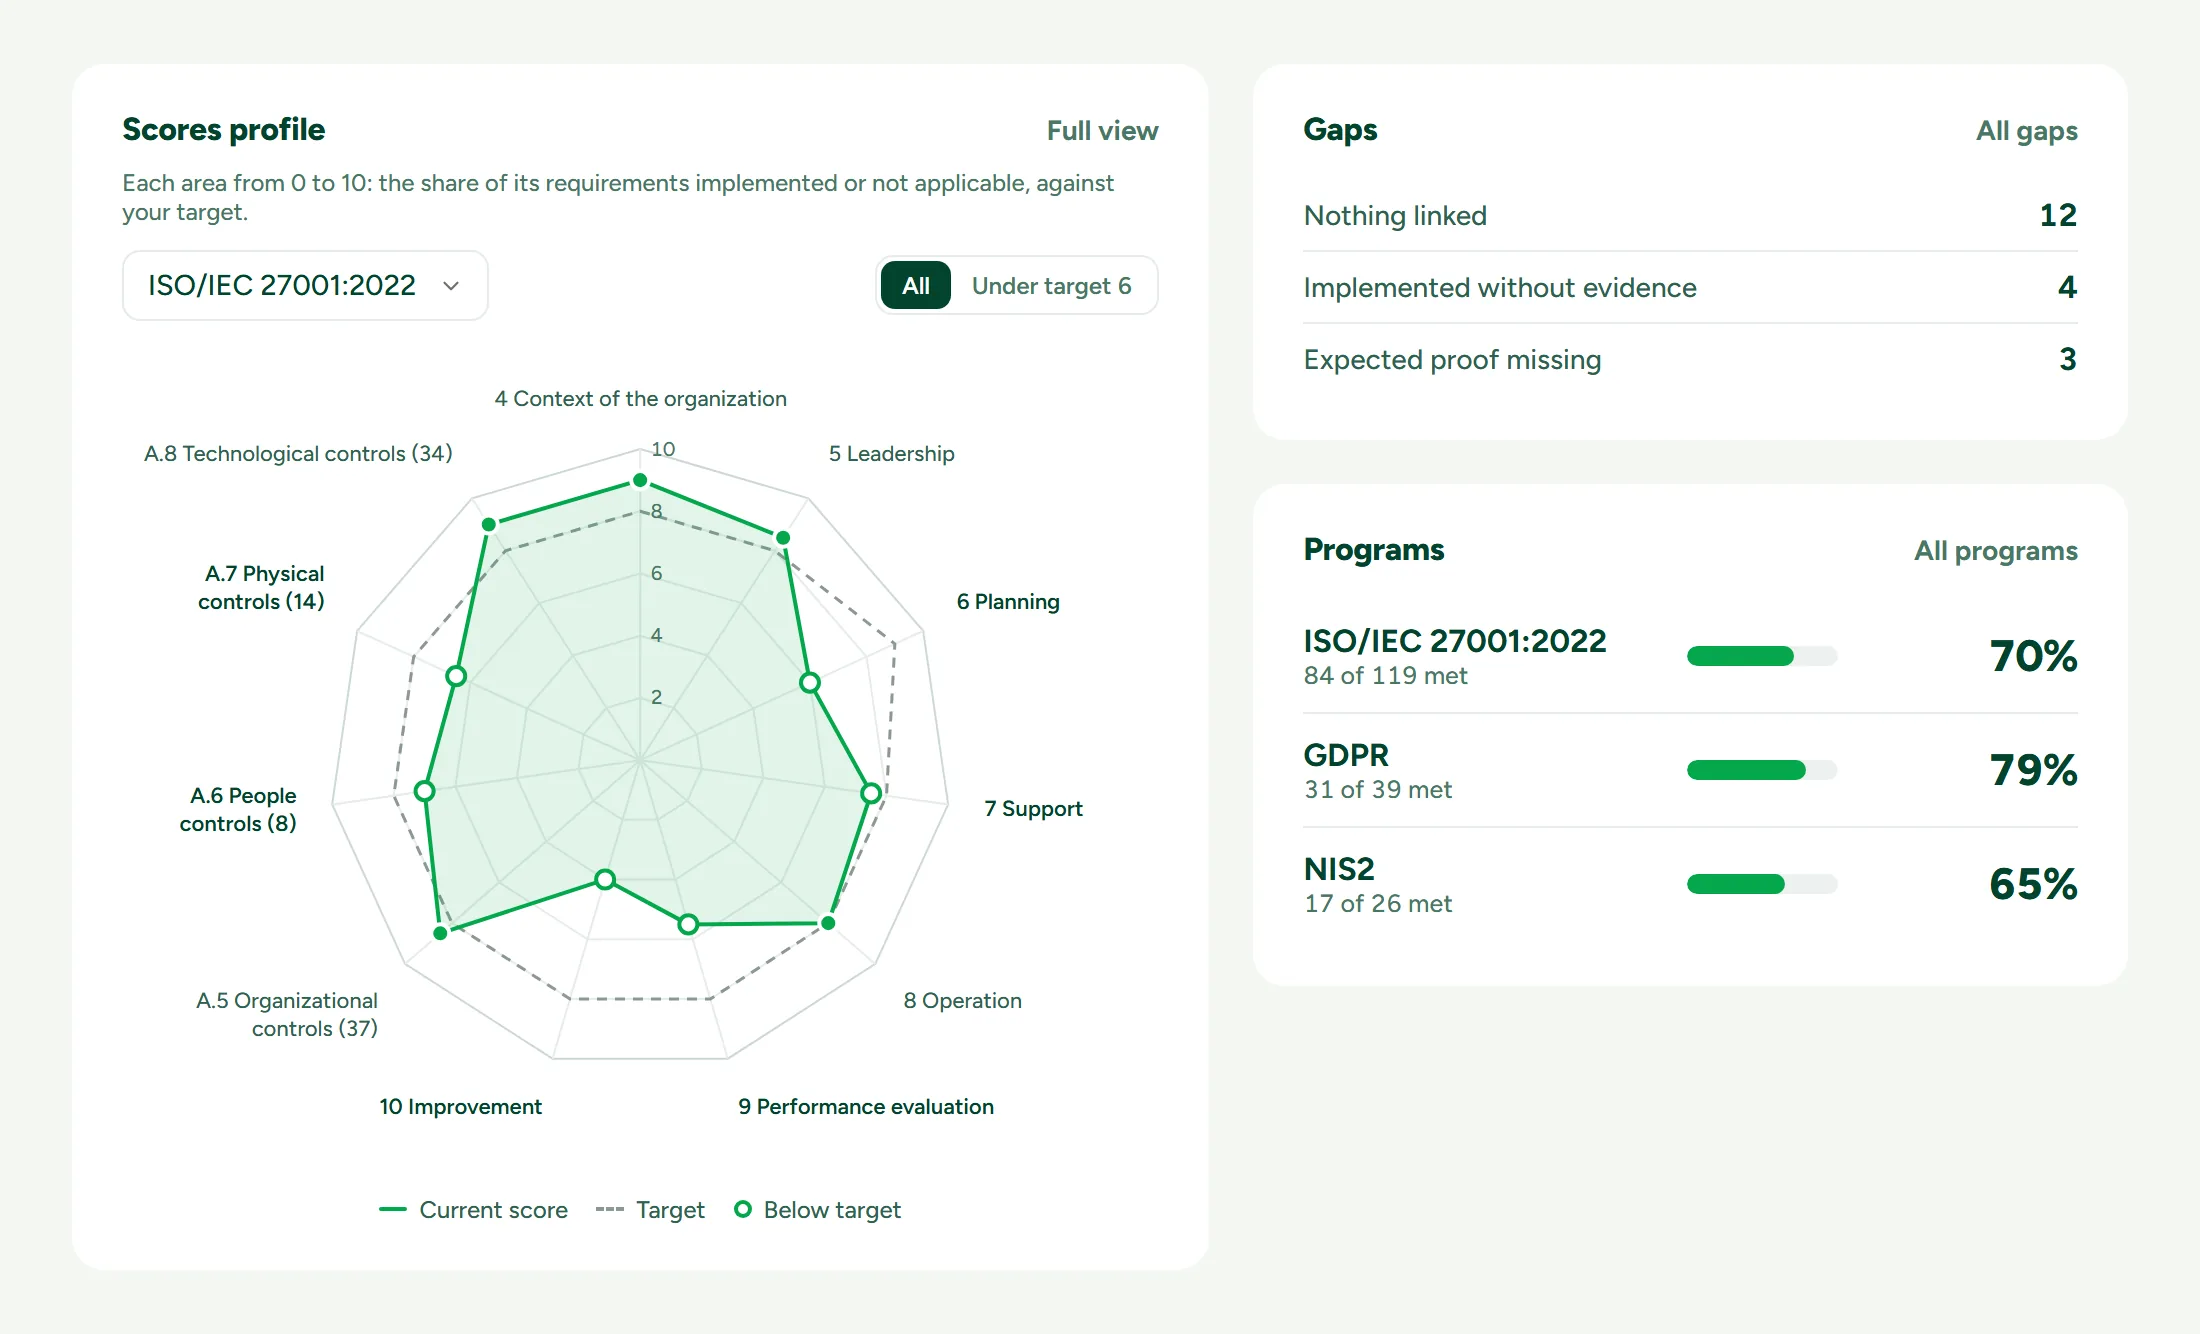
Reports and a board pack as PDF or spreadsheet, sent on a schedule if you want. The Statement of Applicability. A scores profile of each area against your own targets. External auditors get their own login, see only their audit and download an evidence pack.
Every part works on the same records, so a policy or a piece of evidence is entered once and counts wherever it applies.
Thirteen frameworks ready to adopt, and your own on top. A control library based on ISO 27001 Annex A, with test plans and results.
Records of processing, DPIAs, subject requests, breaches, assets, vendors and the DORA ICT register. Each incident shows the GDPR, NIS2 and DORA reporting deadlines that apply to it.
Inherent and residual scores against your risk appetite, scheduled reviews, and formal acceptance with an end date.
Draft, review and publish policies, track who acknowledged which version, and grant exceptions with an end date. Courses with quizzes, assigned by role.
A timeline and agenda of everything with a date, recurring governance activities, a year plan, and reminders by email or as a digest.
Versioned evidence with a fingerprint, the period it covers and a reviewer. Audit request lists, auditor access limited to one audit, and evidence packs.
A report catalogue with a board pack, as PDF or spreadsheet, on a schedule. Gaps, the Statement of Applicability and a scores profile against your targets.
Ask Atitic answers from your own records, and AI connections (MCP) let the AI assistant you already use read them, read-only and per person. Suggested changes wait for a person to accept them. Off until your company turns it on.
Data hosted in the EU, each company isolated in the database, single sign-on, two-factor sign-in, roles per module, and a tamper-evident audit log.
How Atitic protects your records →A compliance or security lead who answers for GDPR and NIS2, a financial entity under DORA, a software company asked for ISO 27001, SOC 2 or ISAE 3402. One workspace for the programs, the registers and the evidence, and a clear view of what is still missing.
Read the in-house story →One login for every client company, each isolated from the others. Start clients from your own Fasttrack presets, see every client’s deadlines in one calendar and their scores side by side, under each client’s own brand.
Read the consultancy story →Run a 5-minute self-check. We email you a readiness score and a list of the gaps that matter most.
Twelve checks across governance, risk management, incident handling and supply chain. For any organization in scope of NIS2.
Start the NIS2 check →Twelve checks against ICT risk management, incident reporting, resilience testing and third-party risk. For financial entities scoped by DORA.
Start the DORA check →Twelve checks across scope + inventory, prohibited practices, high-risk obligations, and transparency + GPAI. For anyone developing or using AI systems in the EU.
Start the EU AI Act check →Free trial. No credit card. EU-hosted.
Create your workspaceBy starting a trial you agree to our Terms of Service and Privacy Policy.